‘Data breach definitely a concern’: SBI Chairman C.S. Setty
/ 2 min read
Investigation is still being carried out; focus will be on containment measures, identify vulnerabilities and remediate them, he said.
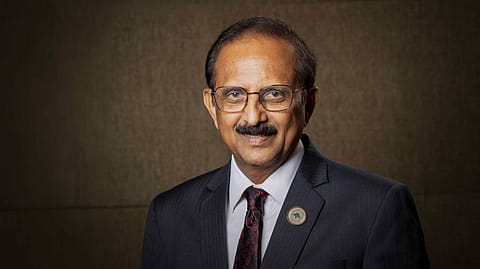
C.S. Setty, Chairman, SBI | Credits: Narendra Bisht
The State Bank of India (SBI) chairman C.S. Setty on Tuesday called the recent data breach at the bank, in which some customers’ data was exposed on the dark web, “definitely an issue of concern”.
“The digital surface area continues to increase,” Setty told reporters while announcing the bank’s September-quarter earnings.
“The root cause analysis is still being done. It will take some time, but our focus was on containment measures, identifying the vulnerabilities that led to the breach and remediating them,” Setty said.
SBI received alerts from its threat intelligence service provider, the Defence Cyber Agency and CERT-In on October 16 that its customers’ data was available on the dark web. Its preliminary analysis of about 3.75 lakh records found 3,897 customer records containing personal information, the Internet Freedom Foundation said in a post on its X account. SBI informed the BSE and NSE about the incident involving the loss of customer data on October 21.
The exposed information included registered mobile numbers, dates of birth, names, gender, email addresses, residential addresses, branch and CIF identifiers, lead IDs, and details linked to loan records.
Steps up cybersecurity checks
Setty said the bank had undertaken a comprehensive cybersecurity drill, including an API sweep and vulnerability assessment. “It is an ongoing process. Obviously, the security of both our systems and customer information is of paramount importance.”
“For us, more than anything, it has strengthened our resolve to ensure that our cybersecurity measures are strong enough to prevent such breaches in the future,” Setty said. He also described the bank’s cyber insurance cover as “comprehensive”, but said SBI did not disclose the extent of its coverage.
In October, SBI inaugurated CyRIS, a cybersecurity centre of excellence, to strengthen cyber defence and threat intelligence across the financial sector.
Setty said it was important to understand emerging tools, given that most banks did not use frontier technologies to tackle AI-related threats. He said the bank needed to focus on addressing emerging AI risks at both the bank and industry levels. SBI is working with other players to create a sandbox environment to test these AI tools.
“We are definitely working to create an environment to adapt to the emerging risk scenario. The Indian banking system is strong as far as the overall cyber framework is concerned,” he said.
In recent weeks, state-run Bank of Baroda has scaled up its cybersecurity framework across technology and processes following a cyber breach in July. The bank told PTI that its total IT defence spending would exceed 10% of its operating profit, citing a senior official.
{{#most-powerful-women-snapshot-individual.slug}} {{/most-powerful-women-snapshot-individual.slug}} {{^most-powerful-women-snapshot-individual.slug}} {{/most-powerful-women-snapshot-individual.slug}} {{#showRanking}} {{current-rank}} {{/showRanking}} {{#photo.0.url}}
{{name}}
Earlier on Tuesday, SBI reported a 14.28% year-on-year increase in standalone net profit to ₹23,038 crore for the second quarter of FY27, compared with ₹20,160 crore in the corresponding period last year.
SBI said its asset quality improved to its best level in more than two decades in the September quarter, with the gross non-performing assets (GNPA) ratio declining to 1.39% and the net NPA ratio falling to 0.36%.
SBI’s domestic net interest margin (NIM) rose to 3.11% in Q2 FY27, up 3 basis points from a year earlier and 11 basis points from the previous quarter. Setty attributed the improvement in NIM to better liability management.
Follow Fortune India
NEXT STORY